Squid Game
Overview
A steganography challenge themed around the Squid Game universe. The investigation chain involves Google dorking to retrieve an invite code, using that code to extract a hidden file via steghide, then analysing the extracted image through stegsolve to locate a hidden pixel — ultimately decoding the final flag from extracted RGB values.
Investigation
Reconnaissance — Google Dorking
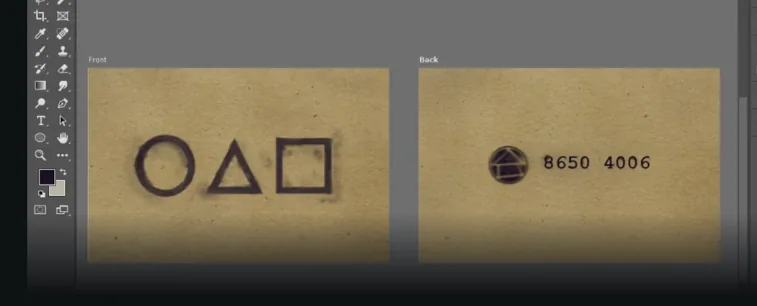
The challenge hints that steghide and stegsolve are required tools. Before touching either, a Google dork against the invitation card reveals the embedded phone number:
Phone number: 8650 4006
This doubles as the steghide passphrase for the next stage.
Steghide Extraction
Install steghide if not already available: sudo apt install steghide
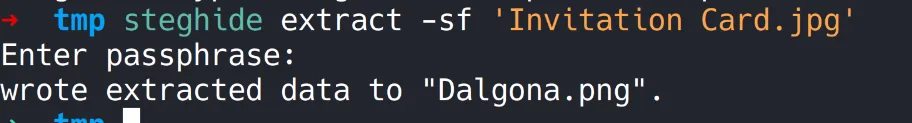 Using the phone number as the passphrase against the invitation card image extracts a hidden file: Extracted file:
Dalgona.png
Stegsolve
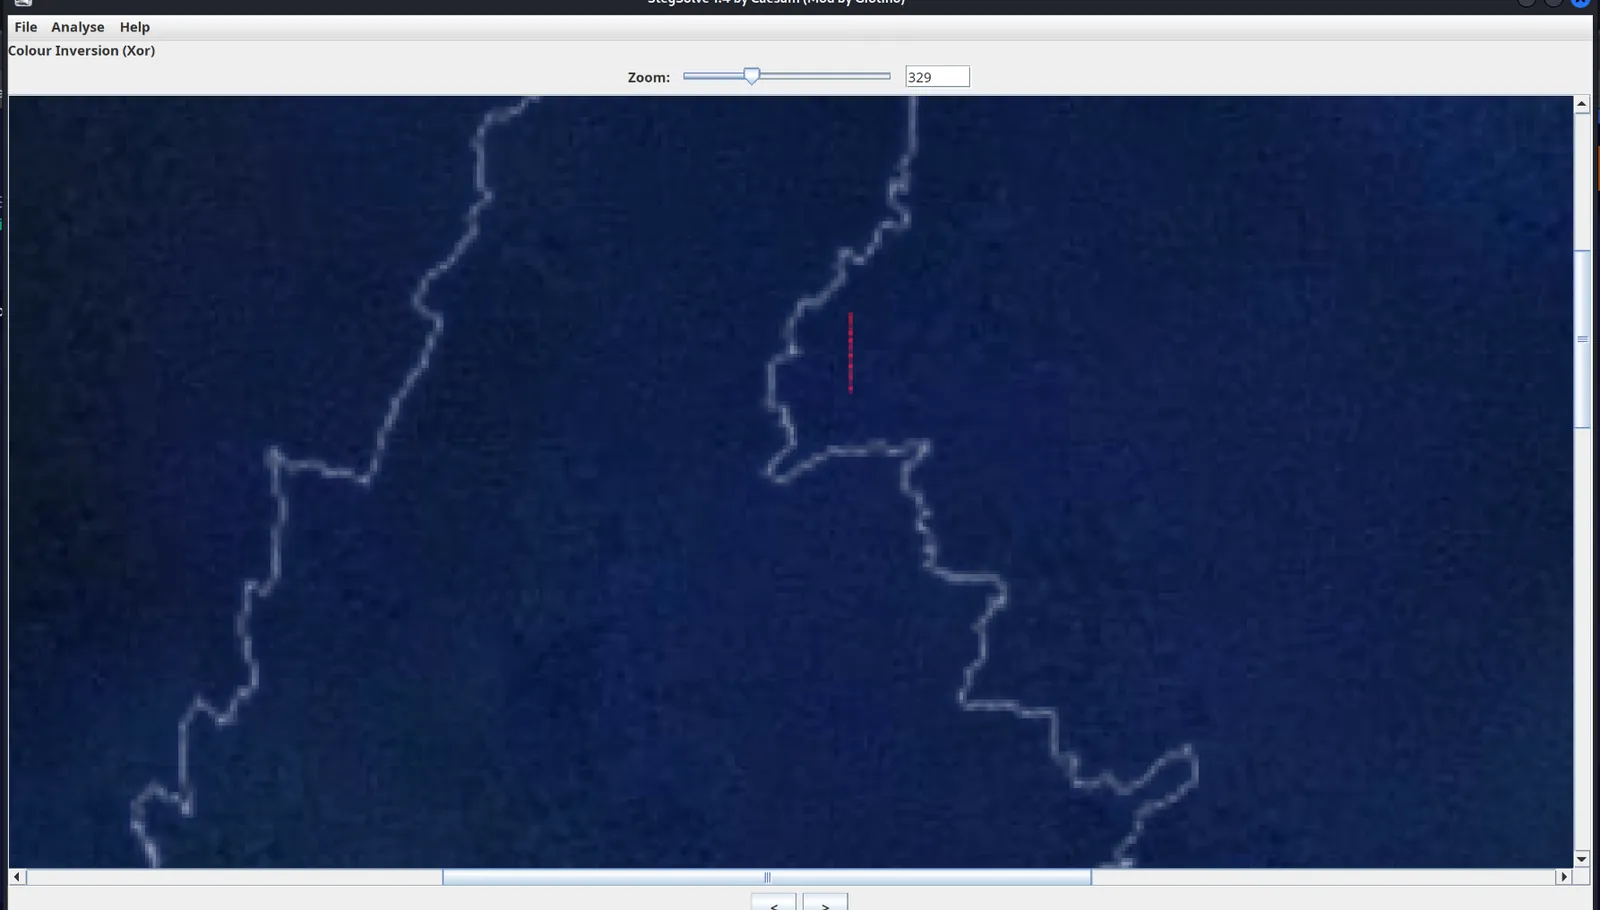
Analysis Opening Dalgona.png in stegsolve.jar (available at github.com/Giotino/stegsolve) and cycling through colour plane filters reveals the hint embedded in the image:
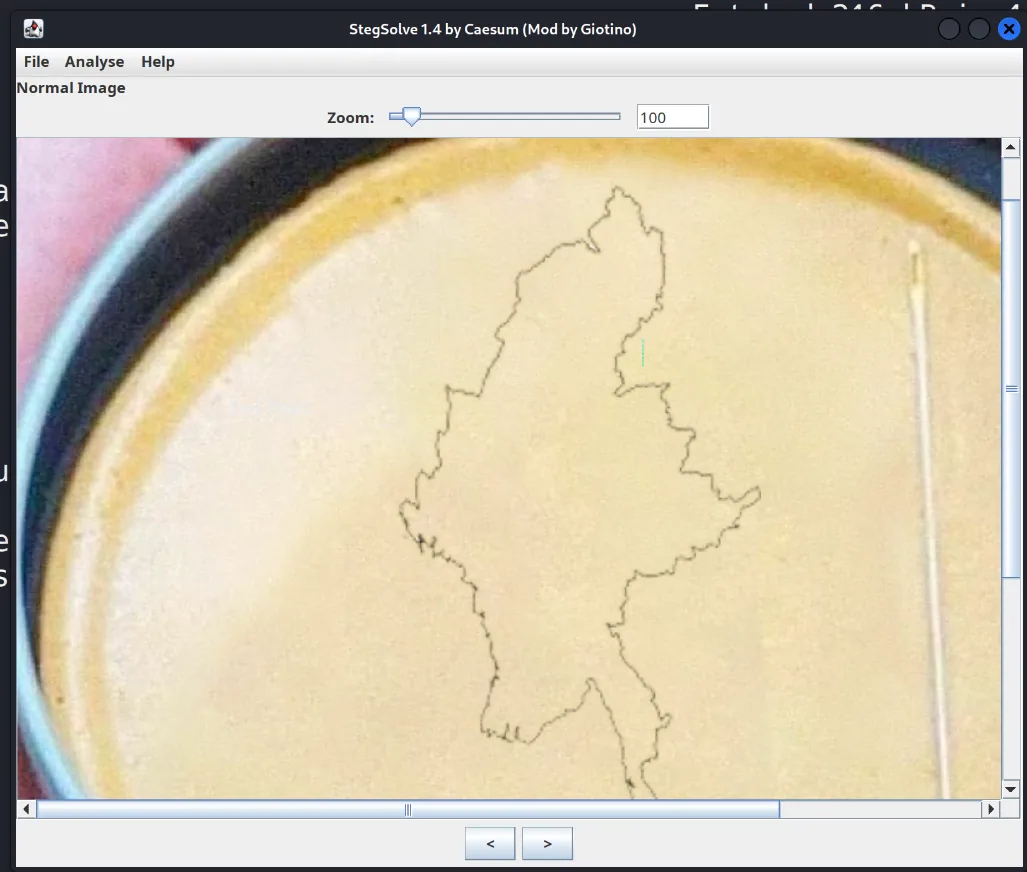 Hint:
red pixel
Pixel Analysis— pixspy.com
Following the red pixel hint, the image is uploaded to pixspy.com to extract the red channel RGB values.
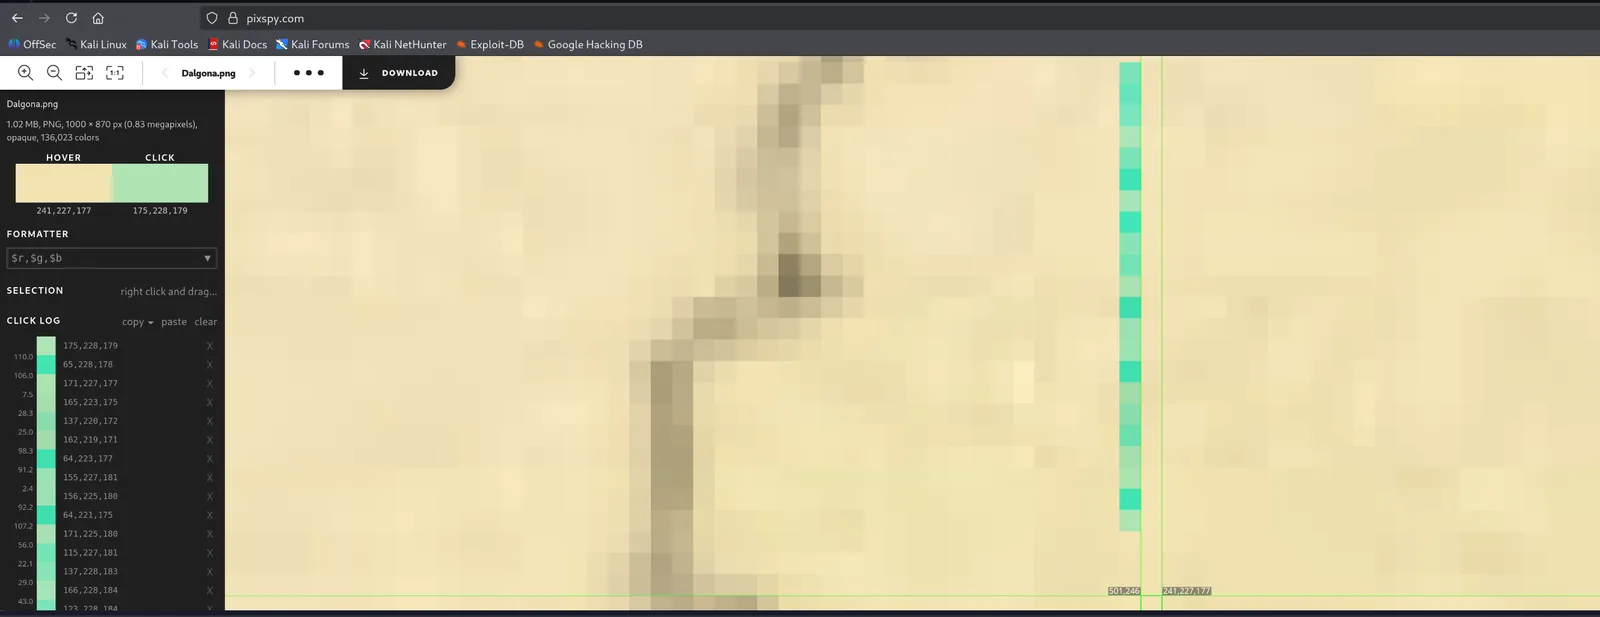 Pulling just the R values produces the following decimal sequence:
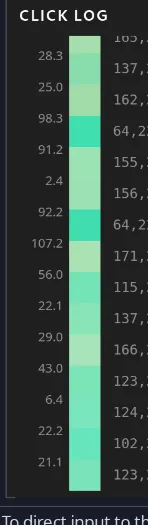
123, 102, 124, 173, 123, 64, 166, 63, 137, 115, 171, 64, 156, 155, 64, 162, 137, 107, 165, 171, 65, 175Decoding — dcode.fr
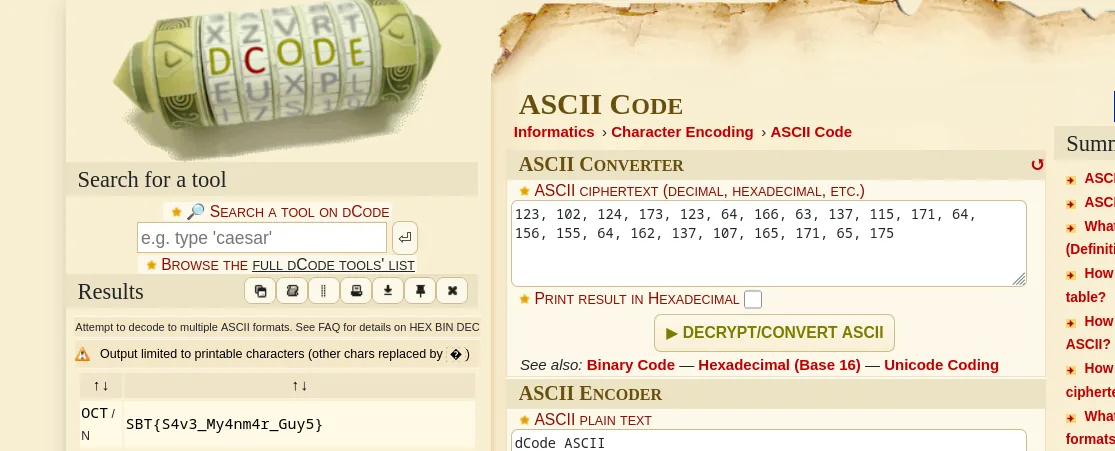
The decimal sequence is submitted to dcode.fr using ASCII decode, which converts the red channel values to the final flag:
Flag: SBT{S4v3_My4nm4r_Guy5}

MITRE ATT&CK
Not applicable — CTF steganography challenge.
Lessons Learned
Steganography challenges follow a predictable chain — recon for credentials, extract hidden data, analyse the output, decode. Google dorking as the first step is an underutilised OSINT technique for surface-level recon. The red channel pixel extraction via pixspy is a useful tool to have in the toolkit for future stego work. dcode.fr remains the go-to for rapid cipher and encoding identification when the encoding type is unknown.